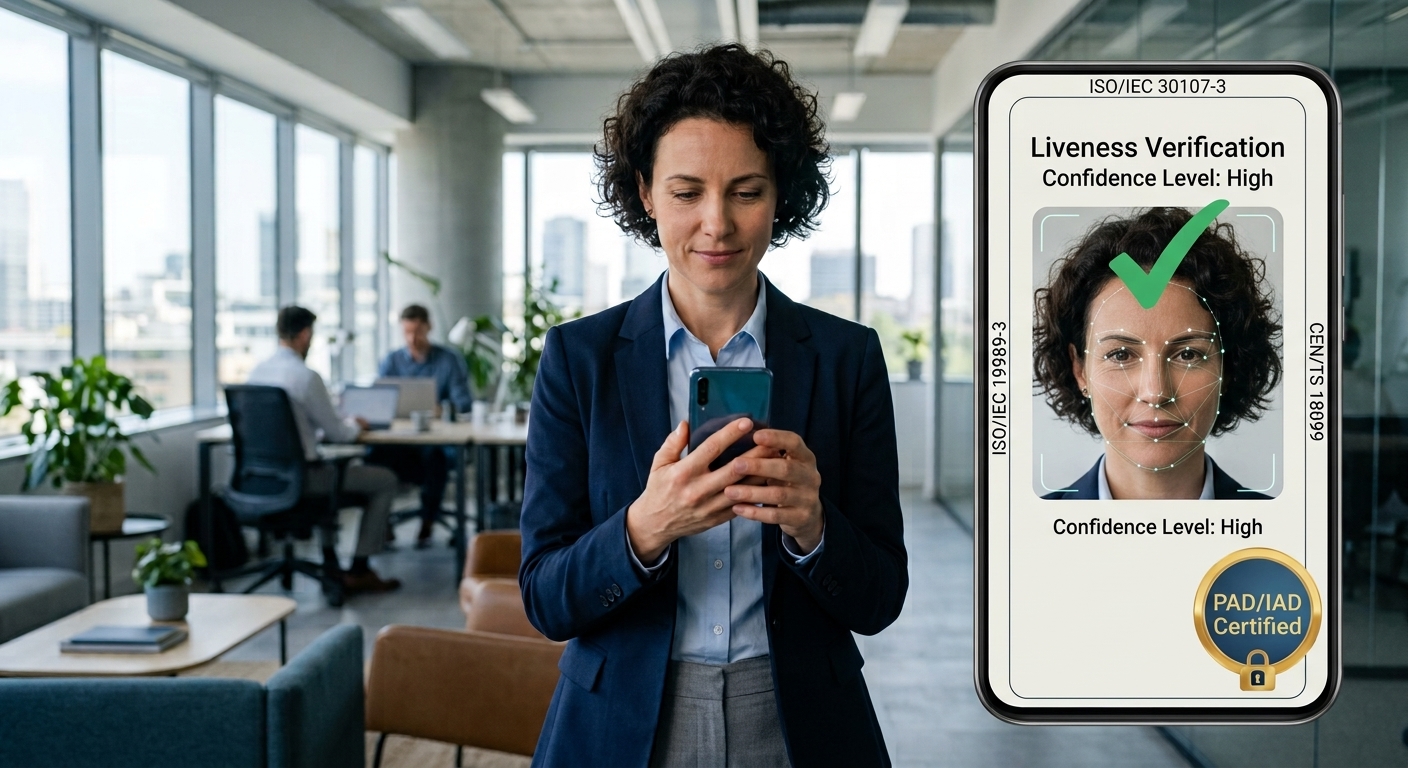
ShareID, a French company specializing in remote identity verification and authentication, announces its high-level compliance certification for the three leading standards in liveness detection (ISO/IEC 30107-3, ISO/IEC 19989-3, and CEN/TS 18099), covering the detection of presentation attacks (PAD) and injection attacks (IAD). The compliance certification was issued on August 19, 2026, by the certification body CLR Cert™, based on a compliance evaluation carried out by CLR Labs, a COFRAC-accredited laboratory that is also an ANSSI-approved evaluation center under the PVID certification scheme, for the ShareID Onboarding Service, which was evaluated at the highest level (High).
Paris, September 22, 2026 - Verifying an identity remotely boils down to answering a question that has become incredibly difficult: Is the person in front of the screen real, present, and truly who they claim to be? Two types of attacks seek to undermine this certainty. Presentation attacks (PAD, Presentation Attack Detection) involve deceiving the camera by using a prop (mask, photo, screen, silicone). Injection attacks (IAD, Injection Attack Detection), which are more recent and have been amplified by deepfakes, simply bypass the camera to inject a hacked stream directly into the system. It is on these two fronts, the most technical and demanding aspects of identity verification, that ShareID has obtained its certification.
Liveness: The Most Scrutinized Aspect of the Audit
In a verification journey, liveness detection is the most difficult step to prove and the one most closely scrutinized by auditors. It is the exact point that distinguishes a physically present person from a sophisticated fraud attempt. ShareID addresses both attack surfaces (PAD and IAD) and has had its components evaluated at a high level in a laboratory according to the three standards considered today to be the reference standards:
- ISO/IEC 30107-3 — the PAD evaluation framework. It defines the methods and measures used to quantify a system's resistance to artifacts presented to the camera.
- ISO/IEC 19989-3 — It establishes the security and evaluation criteria for biometric systems that incorporate this detection technology, in accordance with the Common Criteria.
- CEN/TS 18099 — the specification dedicated to IAD, which addresses the growing threat of stream injection, particularly deepfakes inserted by bypassing the camera.
By achieving high-level compliance with PAD and IAD across these three standards, ShareID demonstrates its resilience against a wide range of biometric attacks: from the most common physical artifacts to deepfakes.
An evaluation conducted by CLR Labs™
CLR Labs™ is an independent evaluation body accredited by COFRAC and also an evaluation center approved by ANSSI (the French National Cybersecurity Agency) under the PVID certification scheme, specializing in the security evaluation of biometric systems. It contributed to the development of the European specification CEN/TS 18099 on the detection of injection attacks, the very standard by which ShareID was evaluated.
Independent evidence that builds trust
Beyond technical performance, this certification provides independent, third-party evidence that ShareID's anti-fraud controls meet the highest standards. For any organization whose operations depend on being certain of its users' identities, this serves as an objective benchmark in a market where promises abound but validations are rare.
These components, which meet the strictest standards, also serve as a foundation that stakeholders can use directly to develop their own ETSI TS 119 461 certification documentation under the eIDAS Regulation.
“With deepfakes and injection tools now widely available, biometric fraud is no longer limited to presenting a photo or a mask in front of a camera: an attacker can now seek to bypass the sensor entirely and inject a fabricated data stream directly into the process. We therefore chose to have our technology evaluated on both of these attack vectors, physical and digital, at the “High” level. For our customers, the key is being able to rely on security that has been measured and evaluated by an independent third party, rather than solely on a technology provider’s promises.”
Sawsen Rezig, CTO and cofounder of ShareID
Learn more
PAD, IAD, deepfakes, liveness: Our next newsletter is dedicated to these threats and how to protect yourself from them. To stay up to date on the latest developments in identity fraud and make sure you don't miss this issue, subscribe to the ShareID newsletter.
About ShareID
ShareID secures remote identity verification and authentication, from the initial customer interaction through to strong authentication. Its proprietary technology, developed in partnership with the French National Gendarmerie, detects document and biometric fraud without storing any personal data. Designed to comply with eIDAS 2.0 and ready for the EUDI Wallet, the solution covers more than 120 countries and can be deployed as SaaS or on-premises.
Contact: marketing@shareid.ai